

What is Sandbox Codex?
Sandbox Codex is the boundary that the operating system enforces around every command Codex runs on your machine: where commands are written to, whether they can reach the network. The approval policy mode is the second layer, deciding when Codex must stop and ask you before crossing that boundary. According to the "Sandbox" and "Agent approvals & security" pages in the Codex documentation (developers.openai.com/codex redirects to learn.chatgpt.com/docs, read 03/11/2026), these two layers are separate but run together. This post makes no promises of any absolutely safe configuration: the documentation itself notes that the network filter layer only reduces rather than eliminates risk, and full-access mode has no protective layer. The post goes through three sandbox modes, approval levels in CLI version 0.162.1, the network, full-access flag, sandbox by operating system, a recommendation table and comparison with Claude Code. General introduction is in the post What is Codex.
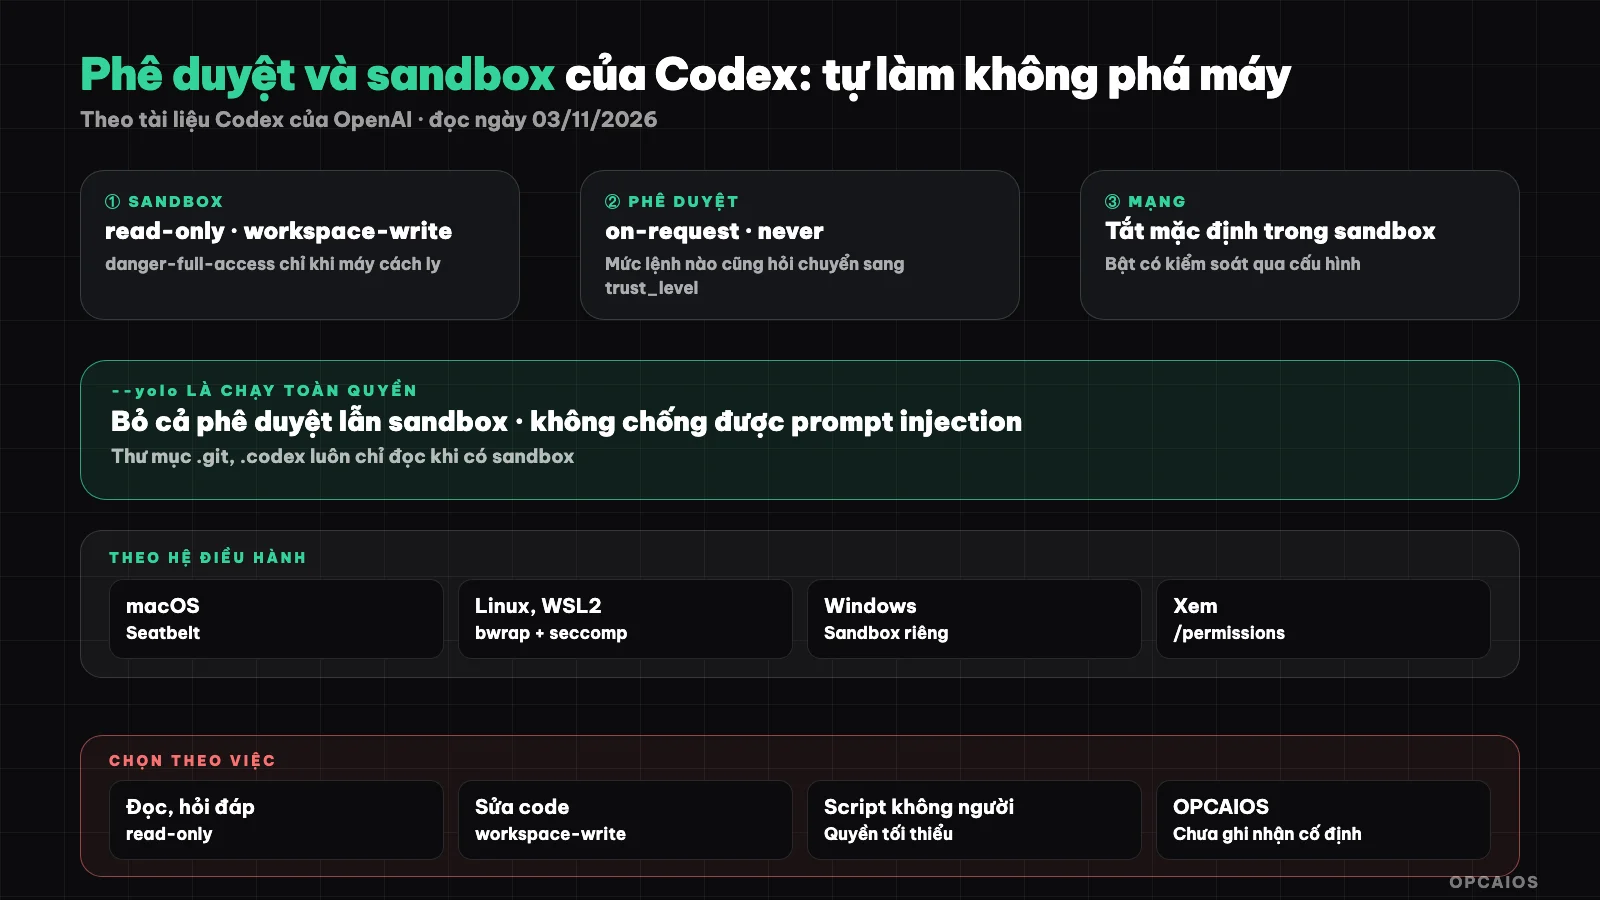
Sandbox sets technical limits, approval mode decides when to ask the person. Diagram: OPCAIOS.
How are the three Codex sandbox modes different?
The three Codex sandbox modes differ in the scope of file writing and network access for commands the model generates. The codex --help command in Codex CLI version 0.162.1 (run on 03/11/2026) lists exactly three values for the -s, --sandbox flag: read-only, workspace-write and danger-full-access. The "Sandbox" page of the Codex documentation describes: read-only only allows reading; workspace-write allows editing in the working directory and running everyday commands, it is the default mode with fewer restrictions; danger-full-access removes all file and network limits. Important point: sandbox applies to all child processes, so git, package managers or test-running commands all inherit the same limits.
| Mode | File writing | Network | When to use |
|---|---|---|---|
read-only |
No | No | Reading unfamiliar code, Q&A, planning |
workspace-write |
Inside working directory and temp directory | Off, unless enabled in config | Everyday code editing |
danger-full-access |
Everywhere | Yes | Only in isolated container or virtual machine |
The documentation also notes that in workspace-write, the .git, .codex, .agents and .aws directories within the write zone are still locked read-only, including everything below them.
What approval levels does Codex currently have?
Codex currently has two selectable approval levels: on-request and never. CLI version 0.162.1 reports an error when you type -a untrusted and only accepts these two values. The "Agent approvals & security" page (read 03/11/2026) confirms that Codex no longer supports approval_policy = "untrusted", and this old value can prevent Codex from starting, so it needs to be removed from config.toml, profile files and scripts. The documentation recommends replacements as follows:
- Want read-only but still get asked: use
read-onlywithon-request. - Want to keep strict rules like before (every command must be approved): remove the approval_policy line, mark the project
trust_level = "untrusted"in the user-level config.toml. - Want to keep some types of questions, auto-reject others: use the
granularpolicy.
codex --sandbox read-only --ask-for-approval on-request
codex --sandbox workspace-write --ask-for-approval on-request
The second line is the Auto preset that the documentation recommends for directories with version control. The --full-auto flag in older tutorial posts is reported as "unexpected argument" by version 0.162.1.
What are auto-review and the /permissions command used for?
Auto-review is a way to pass approval requests that meet conditions to a review agent instead of showing you a dialog box, while keeping the sandbox boundary unchanged. The "Sandbox" page (read 03/11/2026) describes the "Approve for me" option as consisting of workspace-write sandbox, on-request approval_policy and approvals_reviewer = "auto_review"; on CLI this corresponds to the --approve-for-me flag that appears in codex --help. The review agent only examines actions that already require approval (crossing sandbox, calling blocked network, MCP tools with side effects), looks for data leak signs, probes for keys and destruction; if review fails then the action does not run. Auto-review costs extra model calls. In the CLI session, type /permissions to change the permission set being used; the desktop application has a permission selection button right below the input box.
How does network access work in Codex sandbox?
Network access in Codex sandbox is off by default: in workspace-write mode, commands don't go out to the internet until you turn on the network_access = true lock in the [sandbox_workspace_write] section of config.toml. According to the "Agent approvals & security" page (read 03/11/2026), to turn on network while still limiting domains, turn on the network_proxy feature and declare a list of allowed domains. Three rules to remember:
- Turning on proxy when network is off has no effect; turning on network without proxy means commands go out freely.
- The domain list uses a allow-first style, and block rules always win; internal addresses and localhost are blocked by default.
- Proxy doesn't filter web search, MCP tools, browser, Computer Use, or cloud tasks; these have their own switches.
Web search by default uses an index pre-stored by OpenAI instead of loading pages directly, to reduce prompt injection; the --search flag turns on direct search.
Why is Codex's full-power flag dangerous?
Codex's full-power flag is --dangerously-bypass-approvals-and-sandbox, documentation lists the alias --yolo (version 0.162.1 accepts both), turning off all approval prompts and sandbox at once. The description in codex --help calls this flag "EXTREMELY DANGEROUS", only meant for environments already isolated from the outside. It's dangerous because every command the model generates runs straight with your account's permissions: reading SSH keys, sending source code outside, deleting files outside the project are all unblocked. Malicious instructions hidden in READMEs, websites, or issues (prompt injection) no longer need to trick you into hitting approve. Responsible use according to the documentation: run in Docker or Dev Container so the container becomes an isolation layer, then turn on danger-full-access inside.
How does Codex sandbox run on macOS, Linux, and Windows?
Codex sandbox uses the native mechanism of each operating system, so setup and limits differ by machine. Summary from the "Sandbox" and "Agent approvals & security" pages (read 03/11/2026):
| Operating System | Mechanism | What you need to do |
|---|---|---|
| macOS | Seatbelt, runs commands via sandbox-exec with mode-specific profiles |
Use right away, no extra setup |
| Linux, WSL2 | bubblewrap (bwrap) plus seccomp |
Install bubblewrap package; Ubuntu 24.04 may need extra AppArmor profile loading |
| Windows (PowerShell) | Windows native sandbox, prefers MXC, elevated and unelevated versions are legacy fallbacks | Turn on prefer_mxc if your machine and policy support it |
In Docker, Linux sandbox may not run if the container blocks namespaces or seccomp; in that case the documentation recommends leaving isolation to the container. To try a command in sandbox, use the codex sandbox subcommand; the syntax in the documentation and in version 0.162.1 differs slightly, so check codex sandbox --help for your installed version.
Which sandbox and approval settings should I pick for each type of work?
| Type of work | Config suggestion | Reason |
|---|---|---|
| Reading unfamiliar projects, asking about architecture | read-only + on-request |
Nothing gets changed |
| Daily code fixes in git repos | workspace-write + on-request (Auto preset) |
Few prompts, still asks when going out to network or writing outside the project |
| Long tasks, tired of hitting approve | Auto with approvals_reviewer = "auto_review" |
Keeps boundaries, cuts down on prompts |
| Running automated in CI | codex exec --sandbox workspace-write or read-only + never |
No one sits around approving |
| Throwaway experiments | --yolo inside an isolated container |
Only when your machine has nothing to lose |
The table is a suggestion from OPCAIOS, not OpenAI's recommendation. Running without anyone there has its own post: codex exec running automated.
How do Codex permission modes differ from Claude Code?
Codex permission modes differ from Claude Code mainly in the layering: Codex splits into two clear axes (sandbox mode and approval policy), while Claude Code bundles most of it into one permission mode list like plan, acceptEdits, auto, bypassPermissions, with sandbox as an optional feature. In Codex sandbox is on by default; in Claude Code, the documentation says sandbox is off by default. Both have a review layer using the model (auto-review in Codex, a classifier in Claude Code's auto mode) and a mode that skips everything, only meant for inside containers. Details on Claude Code's side in the post plan mode and permission modes in Claude Code; using both at the same time in the post using Codex and Claude Code together.
OPCAIOS Experience
The things below are true, at a conceptual level:
- We have Codex CLI 0.162.x and Codex desktop app on the main work machine, running side by side with Claude Code and Google Antigravity.
- Many project directories are marked as trusted in config.toml. We have not recorded any fixed sandbox mode or approval level set as default for all sessions, so we cannot claim which mode OPCAIOS uses.
- Codex hooks are only used to report session status, with no hooks to block dangerous commands yet. The protection layer remains sandbox, approval, and the owner.
- We have user-level AGENTS.md for Codex, with content equivalent to Claude Code's user-level guidance (respond in Vietnamese, read documentation order at session start, log at session end). This is guidance for the model, not a technical blocking layer.
General principles are in the post security when using AI to write code.
Frequently asked questions
Is Codex sandbox turned on by default?
Yes, according to Codex documentation read on 03/11/2026, the default permission mode applies sandbox by itself, and the network is off by default. Directories using git are usually suggested the Auto preset (workspace-write plus on-request), directories without git are suggested read-only. On Linux and WSL2 you need to install bubblewrap first; if missing, Codex will warn you at startup.
Why does Codex error when I use -a untrusted?
Because Codex has removed the untrusted value from approval_policy. According to the "Agent approvals & security" page read on 03/11/2026, version 0.162.1 only accepts on-request and never, and the documentation says the old value can prevent Codex from starting. Delete that line from config.toml and scripts. If you want to keep the style "ask for every command", set trust_level untrusted for the project in user-level config.toml instead of setting approval_policy. The --full-auto flag in old guidance posts is also gone in this version.
Is it safe to turn on network for Codex?
Turning on network raises risk, because a misdirected command could send code or keys outside. The safer way is to turn on network_access with network_proxy and only allow the exact domains you need, for example your package manager registry. Do not put real keys in the prompt, and review the command log after the session.
When can I use --yolo?
Only when the machine running Codex is already isolated from outside, for example a Docker container or Dev Container with no real keys and no important directories mounted. On an everyday work machine, this flag removes all protection layers. If you just hate clicking approve many times, try auto-review first: keep the sandbox and cut down the dialog boxes.
What mode should someone with no coding knowledge pick?
Start with read-only to ask Codex to explain the project, then switch to the Auto preset once you understand what needs doing, always working on a repo with git. The full process is in the post programming agent for people who don't know code. If you want someone to guide you through real work, see OPCAIOS's AI application training course.
Source: Codex documentation from OpenAI, pages "Sandbox" and "Agent approvals & security" (developers.openai.com/codex redirects to learn.chatgpt.com/docs/sandboxing and learn.chatgpt.com/docs/agent-approvals-security), plus codex --help version 0.162.1, read on 03/11/2026; have not run sandbox tests myself on Linux and Windows; flag names may change by version; the mode table is a suggestion. The experience is OPCAIOS's.
Translated from Vietnamese with AI. Read the original.
Want to apply this in your business?
Book a free 30-minute call (Vietnam time, in English or Vietnamese).