

Using Codex for Code Review
What is using Codex for code review? Using Codex for code review means having OpenAI's Codex programming agent read the changes (diff) of a branch, a commit, or a pull request and report potential errors before you merge, either using the /review command on your machine or by commenting @codex review on GitHub. This post does not claim that Codex code review catches every error, nor do we treat AI feedback as a guarantee of quality: we have no data on Codex's error detection rate, and the documentation we read does not provide that number either. To be clear from the start: OPCAIOS does not use Codex code review regularly; the how-to section is based on official documentation and the --help output of Codex CLI version 0.162.1, read on 03/11/2026. The post covers: review on your machine, review on GitHub, review criteria, what AI often misses, a reviewer's checklist, and how to combine it with testing. New to the tool? Read What is Codex.
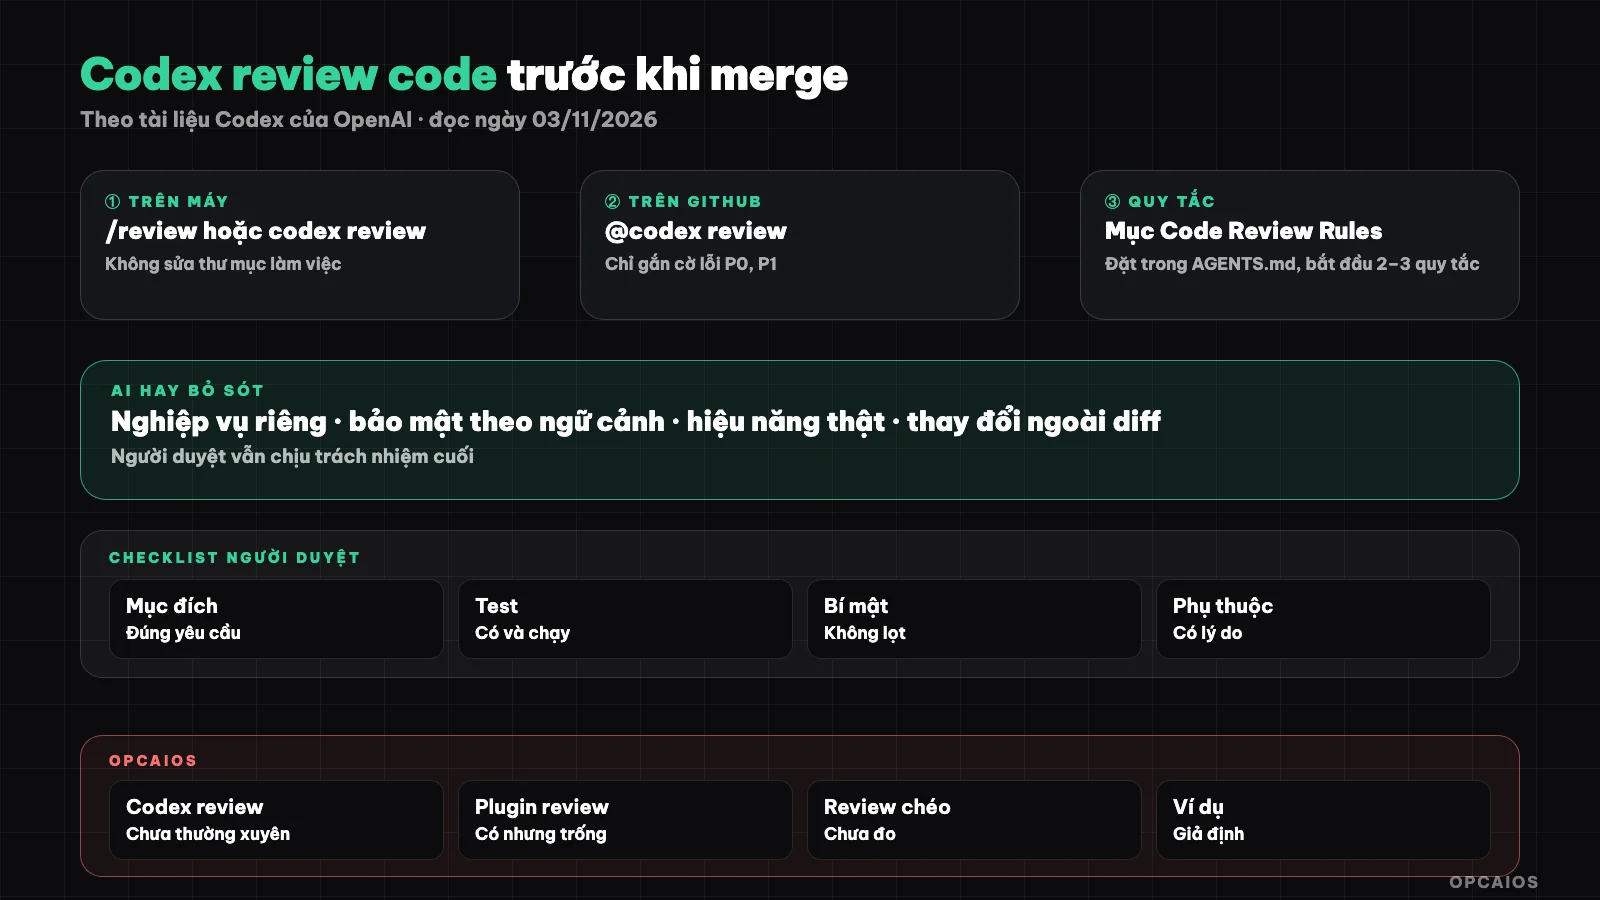
Automated tests catch machine errors, Codex scans the diff, the reviewer decides whether to merge. Diagram: OPCAIOS.
What can Codex's /review command do on your machine?
The /review command is how you start a code review session directly in Codex CLI, the Codex desktop app, or IDE extensions, without pushing code to GitHub. According to the "Code review" page on learn.chatgpt.com/docs (read on 03/11/2026, developers.openai.com/codex redirects there), Codex CLI offers 4 options when you type /review:
- Review against a base branch: Codex finds the merge base and reviews the entire diff of your branch against the base branch.
- Review uncommitted changes: review staged changes, unstaged changes, and untracked Git files.
- Review a commit: review only the changes in a specific commit.
- Custom review instructions: review according to criteria you write yourself.
The desktop app and IDE extensions only have the first 2 options, and the command only appears when your project is in a Git repository. According to the documentation, review does not modify your working directory—it only reports prioritized findings. The review_model key in the config file lets you use a different model just for reviews.
Is there a non-interactive review command?
Yes. codex review --help on Codex CLI version 0.162.1 shows that the codex review command runs a review without opening a chat window, with flags like --uncommitted (uncommitted changes), --base <BRANCH> (compared to a base branch), --commit <SHA> (a single commit), and --title (title in the summary). The command also accepts review criteria as text. The documentation we read does not describe this command, so details come only from the help text.
codex review --base main
codex review --uncommitted "Focus on checking access control and error handling"
How do you attach Codex to a pull request on GitHub?
Attaching Codex to a pull request means enabling Codex's Code Review feature for a connected GitHub repository so Codex automatically posts a review on your pull request. According to the "GitHub" page in the integrations section of Codex documentation (read on 03/11/2026), the steps are:
- Connect your GitHub repository with Codex.
- Open the Codex code review settings page at chatgpt.com/settings/code-review, select your repository, and enable Automatic review in the Review code section if you want every pull request reviewed.
- To auto-review your own pull requests, enable Automatic review in Personal preferences and choose the activation type.
- If you don't enable automatic review, comment
@codex reviewon the pull request; you can add a focus area, for example@codex review for issues in the database migration.
You need push or admin permissions on the repository. The documentation states that Codex only flags P0 and P1 errors on GitHub to keep comments focused on high-risk issues. There is also a @codex security review command for security reviews, with full results available in the Security Report tab of the task. This page does not specify ChatGPT plan requirements.
How to Write Review Criteria for Codex So It's Useful?
Review criteria is a short list of things you want Codex to scrutinize, placed in an AGENTS.md file so every review uses the same criteria. Codex's GitHub documentation recommends adding a ## Code Review Rules section to the nearest AGENTS.md file to the code that the rules govern, using ### to group checks; for each changed file, Codex applies rules from the root file plus the most specific rules. The documentation recommends starting with 2 to 3 short rules and leaving mechanical checks like formatting and lint to CI. See also what AGENTS.md is. Example for a course-selling website:
## Code Review Rules

### Payment
- Every change in payment webhook handling code must verify the signature and prevent duplicate processing.

### Access Control
- Paid content must never be sent to the browser before checking permissions on the server.
Good criteria clearly state business risks, can be verified by reading code, and are specific enough.
What Does Codex Often Miss When Reviewing Code?
Codex often misses errors that need information outside the diff, and this is a reasoned observation rather than a measurement result from us. An agent only sees the changed part, the code it chooses to read further, and the criteria you give; it doesn't know how real users operate the product or how large the real data is. Three groups need human scrutiny:
- Business context: code is technically correct but violates business rules, for example discounts stacking when they shouldn't, or changing order status without sending an email. AI only knows rules if they're written down.
- Security: vulnerabilities often sit at the junction of multiple parts, like a new route forgetting to check permissions or an environment variable being logged. See security when using AI to write code.
- Real performance: a query runs fast with 50 rows of test data but may be slow with real data; AI doesn't see table sizes or actual throughput unless you provide numbers.
Also, AI findings can be wrong; cross-check each finding against the specific lines of code it points to.
Checklist for Reviewers to Check After Codex
The reviewer's checklist is the final step that AI cannot replace, because the reviewer is responsible for deciding to merge. Here's a suggested checklist to use after Codex has run:
- Read the pull request description: does the diff do what's stated, nothing more, nothing less.
- Read the actual diff, not just AI's summary.
- For each Codex finding, open the corresponding code line and confirm the error is real.
- Check related business rules: pricing, permissions, status, customer notifications.
- Check sensitive data: secrets, personal information, paid content not exposed.
- Check database changes: can they be rolled back, do they lock tables for long.
- Ask about performance: how many rows does the new query run on, are there network calls in loops.
- Confirm automated tests have run and passed, including new tests for the changed part.
- Record the reason for merging or not merging.
Someone who can't code can still do steps 1, 4, 5, and 9; see also safe process for non-coders.
How to Combine Codex Review with Automated Tests?
Combining Codex review with automated tests means dividing work: tests and lint catch mechanical errors, repeatable ones; Codex scrutinizes logic and risks in the diff; the reviewer decides. Suggested order:
| Layer | Catches | Who runs |
|---|---|---|
| Lint, type check, formatting | Syntax errors, type mismatches, style | CI, every push |
| Automated tests | Known behavior breaking | CI, every pull request |
| Codex review | Wrong logic, edge cases, P0/P1 risks | /review locally or @codex review |
| Human reviewer | Business rules, security in context, real performance | Project owner |
When Codex finds a real error, ask for a test to reproduce the error before fixing. To run Codex in CI, see codex exec running automatically; the sandbox mode determines what Codex can do, see Codex approval and sandbox modes.
OPCAIOS's Experience
OPCAIOS doesn't use Codex review code regularly, and we're being straightforward so this post doesn't cause misunderstanding. The main work machine has Codex CLI version 0.162.x and the Codex desktop application, used alongside Claude Code and Google Antigravity. There's a directory for Codex's code review plugin on the machine but it's empty. We once asked another agent to review changes for us, but haven't measured how well it worked, so we don't have numbers on how many bugs were caught. One lesson from having multiple agents fix the same system (see multiple AI sessions fixing one project): some bugs fall completely outside logic—for example, deploying from a Windows machine once changed over 1,500 files just because of line break style. Looking at the number of changed files before reading the details helps catch this type of bug early.
Frequently Asked Questions
Can Codex review code replace human review?
No. Codex review code scans diffs quickly and points out P0, P1 risks, but only knows what's in the code and the rules you write down. Business rules not written down, real data or agreements with customers are outside its view, and its findings can be wrong. Use Codex as a second reader; the decision to merge is still the responsibility of whoever owns the product.
Does the /review command fix code automatically?
According to Codex's documentation page "Code review" (read on 03/11/2026), review doesn't change the working directory: Codex only reports findings it has prioritized. To fix, you ask again in the same session, and at that point the sandbox mode and approval mode you're using still apply. The safe way is to read each finding, pick the ones that are real, then let Codex fix them on a separate branch.
Why doesn't Codex comment on small bugs on GitHub?
The GitHub integration documentation says Codex only flags P0 and P1 level bugs to comment so discussion focuses on high risk. So no comment doesn't mean the pull request has no small bugs. Format bugs, naming, style should go to lint and formatter in CI. If you want Codex to pay attention to a specific area, add focus after @codex review, or write a rule in the Code Review Rules section of AGENTS.md.
How many review rules should I write in AGENTS.md?
Codex documentation recommends starting with 2 to 3 short rules then adding gradually. Rules should tie to real business risk in your project, like payment, access, personal data, and go in AGENTS.md near the most related code. After each bug slips through review, think about adding a rule or a matching test.
Can someone who doesn't know code use Codex review?
Yes, at a support level, if you treat the results as a list of questions to check rather than a verdict. Ask Codex to explain each finding in plain language, point out the line of code and what it means for customers. What you do best is checking business rules, sensitive data and the reason to merge. To get guidance on safe review process by real project, see OPCAIOS's AI application training course.
Source: Codex documentation from OpenAI, pages "Code review" and "GitHub" at learn.chatgpt.com/docs (developers.openai.com/codex redirects there), and codex review --help from Codex CLI version 0.162.1, read on 03/11/2026; example review rules and course sale website are assumptions; haven't verified ChatGPT Code Review package terms, haven't measured Codex's bug catch rate, haven't run the review commands in this post on OPCAIOS's repository. The experience is OPCAIOS's.
Translated from Vietnamese with AI. Read the original.
Want to apply this in your business?
Book a free 30-minute call (Vietnam time, in English or Vietnamese).