

What Is a 24/7 AI Agent?
It is a program that uses a language model to receive tasks, make plans, call tools, and report results, running continuously on a server instead of only answering when you open a chat window. For a solo business owner, "24/7" only has value when the system has three things: a stable place to run, limited permissions, and an alert mechanism when something goes wrong. Without these three, an agent running at night is just a nighttime risk.
Example scenario: Anthropic's Claude agent synthesizes news and sends a report each morning, running 24 hours a day on a VPS, but only writes to a drafts folder and sends alerts via Telegram. This post describes the minimal architecture, what to delegate, how to limit permissions, monitor, handle when the agent makes mistakes, and the real limitations of OPCAIOS.
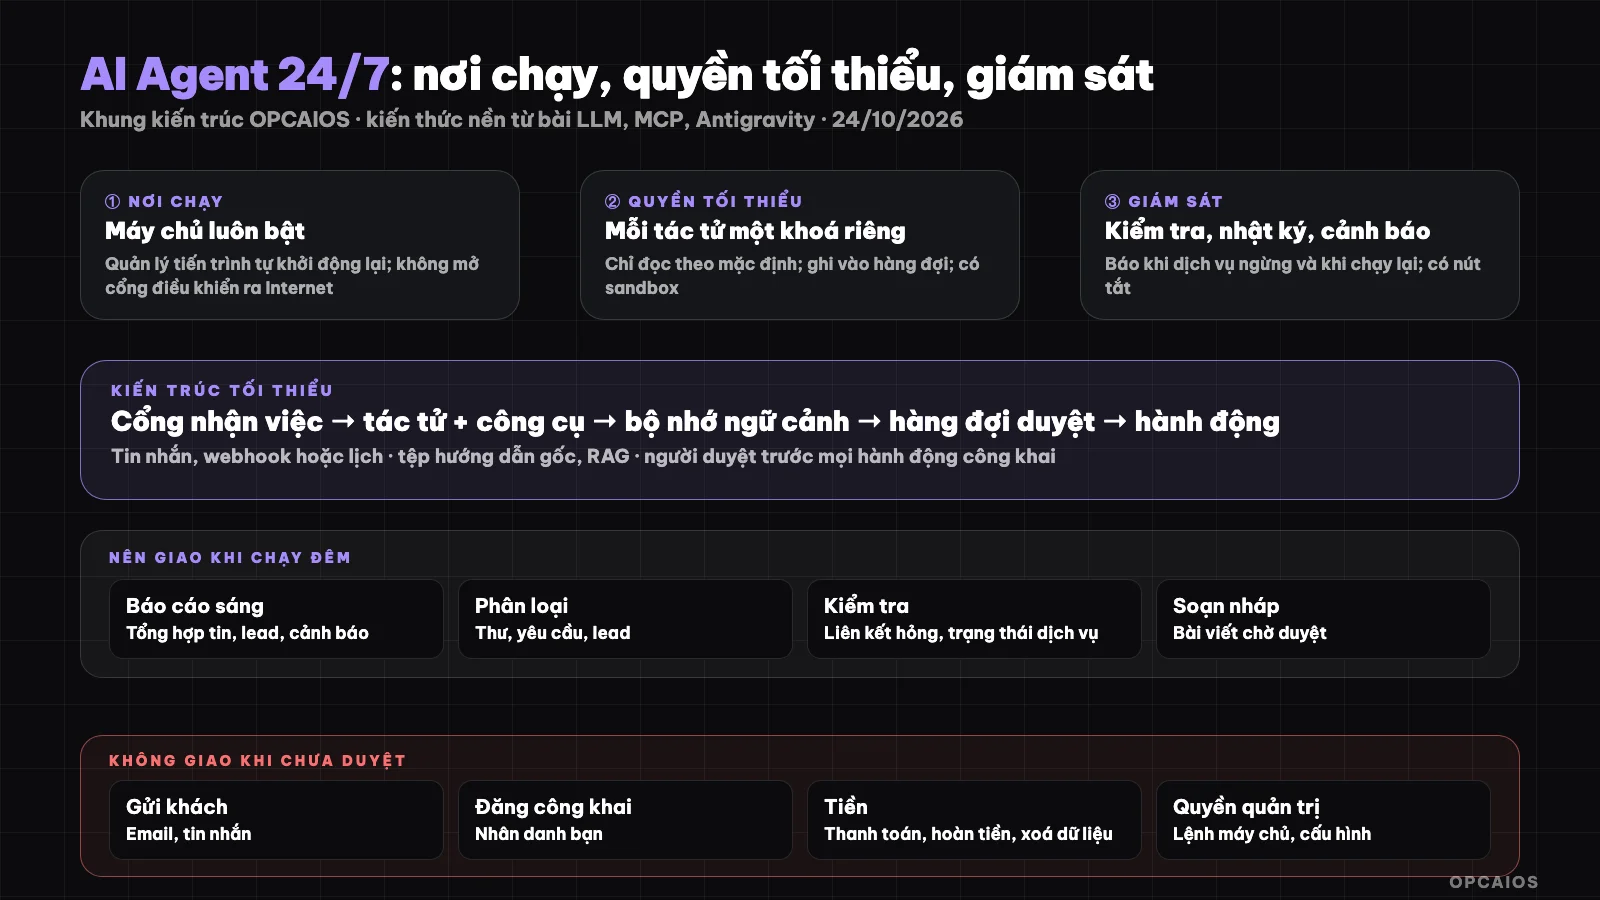
An agent running continuously needs a stable place to run, minimal permissions, monitoring, and a reviewer. Diagram: OPCAIOS.
How Is an Agent Different From a Chatbot?
An agent is a program with a goal that breaks work into steps by itself, while a chatbot only answers when asked. An agent calls tools like reading files, calling APIs, or running commands, sees the results, then decides the next step (see What Is LLM? about tool use and agents). Anthropic's MCP protocol standardizes how to connect an agent with tools. For example, ChatGPT or Claude in chat form only drafts an email when asked, while an agent can read the mailbox at 6 a.m., sort 50 emails, and send a summary via Telegram. An agent is more powerful but also riskier: an agent can make mistakes many times very quickly, so it needs minimal permissions and a reviewer.
What Does the Minimal Architecture for an Agent Running Continuously Include?
The minimal architecture has six components: place to run, job entry port, agent and tools, context memory, monitoring, and reviewer. The table below is OPCAIOS's advisory framework, not an industry standard.
| Component | Role | Suggestion |
|---|---|---|
| Place to run | Always-on machine | A private server (see What Is VPS?) or hosting service; manage the process to auto-restart |
| Job entry port | Receive commands from you | Messages (e.g. Telegram bot), webhook, scheduled tasks |
| Agent + tools | Do the work | Only grant needed tools; each tool has its own permission |
| Memory, context | Know you and your business | Base instruction files, note repository, RAG (see What Is Second Brain? and What Is RAG?) |
| Monitoring | Know when it breaks | Periodic health checks, alerts through a channel you read immediately |
| Reviewer | Block risk | Queue waiting for approval before any public action or irreversible action |
What Work Should and Should Not Be Delegated to a Nighttime Agent
Should delegate: morning news synthesis and reporting, email and lead sorting, draft writing, broken link checking, price or competitor tracking, backup and service status checks.
Should not delegate without approval: sending email or messages to customers, posting public content, payment or refunds, deleting data, changing server configuration, running admin commands.
How to Limit AI Agent Permissions for Safety?
Limiting permissions is the most important principle, because an agent running at night has no one watching. The six rules below are ranked by priority; first is minimal permissions, last is not opening control ports to the Internet. Example scenario: the agent only has the read-only API key of one service and writes to a drafts folder, so even if it fails 100 times in one night it cannot send any email to customers.
- Minimal permissions: each agent has its own account and API key, only enough for its task; do not use admin keys.
- Read-only by default: write to a drafts folder or queue, reviewer approves then applies.
- Sandbox and network limits: run commands in an isolated environment when possible; see recognized risks in approval-free command mode in What Is Antigravity 2.0?.
- Do not put secrets in prompts or the knowledge base that the agent reads.
- Limit spending: set a token or budget limit per month and alert when near the cap.
- Do not open control ports to the Internet: access through SSH tunnel or VPN with authentication.
Monitoring and alerting
- Check main services regularly (agent, database, job queue) and alert when they stop and restart.
- Structured logs: who did what, when, and the result; for tracing when something goes wrong.
- Alerts where you read them immediately, like Telegram, with a link to the logs.
- Test regularly with a sample job to know the agent is still working right.
When the agent goes wrong
- Stop the agent (with a clear kill switch).
- Check the logs to see what it did.
- Rollback from backup if needed.
- Narrow permissions or add a review step at the exact point where it failed.
- Write down the lesson in a rules file so later runs don't repeat it.
OPCAIOS's experience
According to OPCAIOS's internal operations document, our system has an orchestration agent running on a Mac and an execution agent running on a private server, talking through a shared state file and Telegram. We have a service check every few minutes with Telegram alerts when a service stops or restarts, a queue waiting for review on public content, monthly token limits, and a rule against embedding secrets in the knowledge base. We've also hit real limits: some parts (like shared long-term memory) have gone down before, and the multi-agent flow over webhooks hasn't run yet, so the document says "check before trusting" instead of treating it as always on. We don't have a number for the rate of tasks that complete right on their own, so we didn't put efficiency numbers in this post.
Frequently asked questions
What's a 24/7 AI agent?
A 24/7 AI agent is a program that uses a language model like Claude from Anthropic or GPT from OpenAI to take jobs, call tools, and report results, running all the time on a server, with monitoring and limits on what it can do. First, the agent gets a job via Telegram message or a schedule. Next, the agent breaks the job into steps and calls tools. Finally, the agent reports the result and waits for a person to review any public actions. Example: a morning report is written at 6 am, and the business owner reviews it in 5 minutes.
What's the minimum to run a 24/7 agent?
You need at least six parts to run a 24/7 agent: a place to run it that's stable, a job queue, context memory, least privilege, monitoring, and a person to review. Example: a VPS for a few dollars a month, a separate API account with monthly limits, and a Telegram alert is enough to try, but monitoring and review can't be skipped.
Is it safe to let the agent run at night?
Only if you limit what it can do, have a sandbox, alerts, and a review queue. Don't let the agent email customers, post publicly, or charge money without review first.
How is an agent different from regular automation?
Regular automation runs a fixed script, like n8n sending email when a new form comes in. An agent plans each step, so it's more flexible but harder to predict. For example, when a customer asks an odd question, an n8n workflow fails at a step not in the flow, but an agent can find info and draft a reply for review. So many systems use both: n8n handles fixed parts, the agent handles edge cases. To learn how to build a safe agent, see OPCAIOS's AI application training.
Source: knowledge of agents and tools from OPCAIOS's posts on LLM, MCP, Antigravity (read 24/10/2026); the architecture and permission principles are OPCAIOS's advisory framework, not an industry standard. The experience is OPCAIOS's from our internal operations document.
Translated from Vietnamese with AI. Read the original.
Want to apply this in your business?
Book a free 30-minute call (Vietnam time, in English or Vietnamese).