

What is VPS?
VPS (Virtual Private Server, virtual private server) is a virtual machine sold by a hosting provider as a service: it runs your own copy of an operating system and you typically have superuser (root) privileges on that operating system, so you can install most software that runs on that operating system. According to Wikipedia, in many ways VPS is equivalent to a dedicated physical server but easier to create and configure and cheaper; in exchange, VPS instances share underlying hardware so performance can be lower depending on the load of other virtual machines. This post explains what VPS is, how it differs from shared hosting and PaaS platforms, how to choose a VPS, a basic security checklist (SSH, firewall, Docker, TLS, Cloudflare), how to operate a website, backups and monitoring, and real experience from OPCAIOS when running a website on VPS.
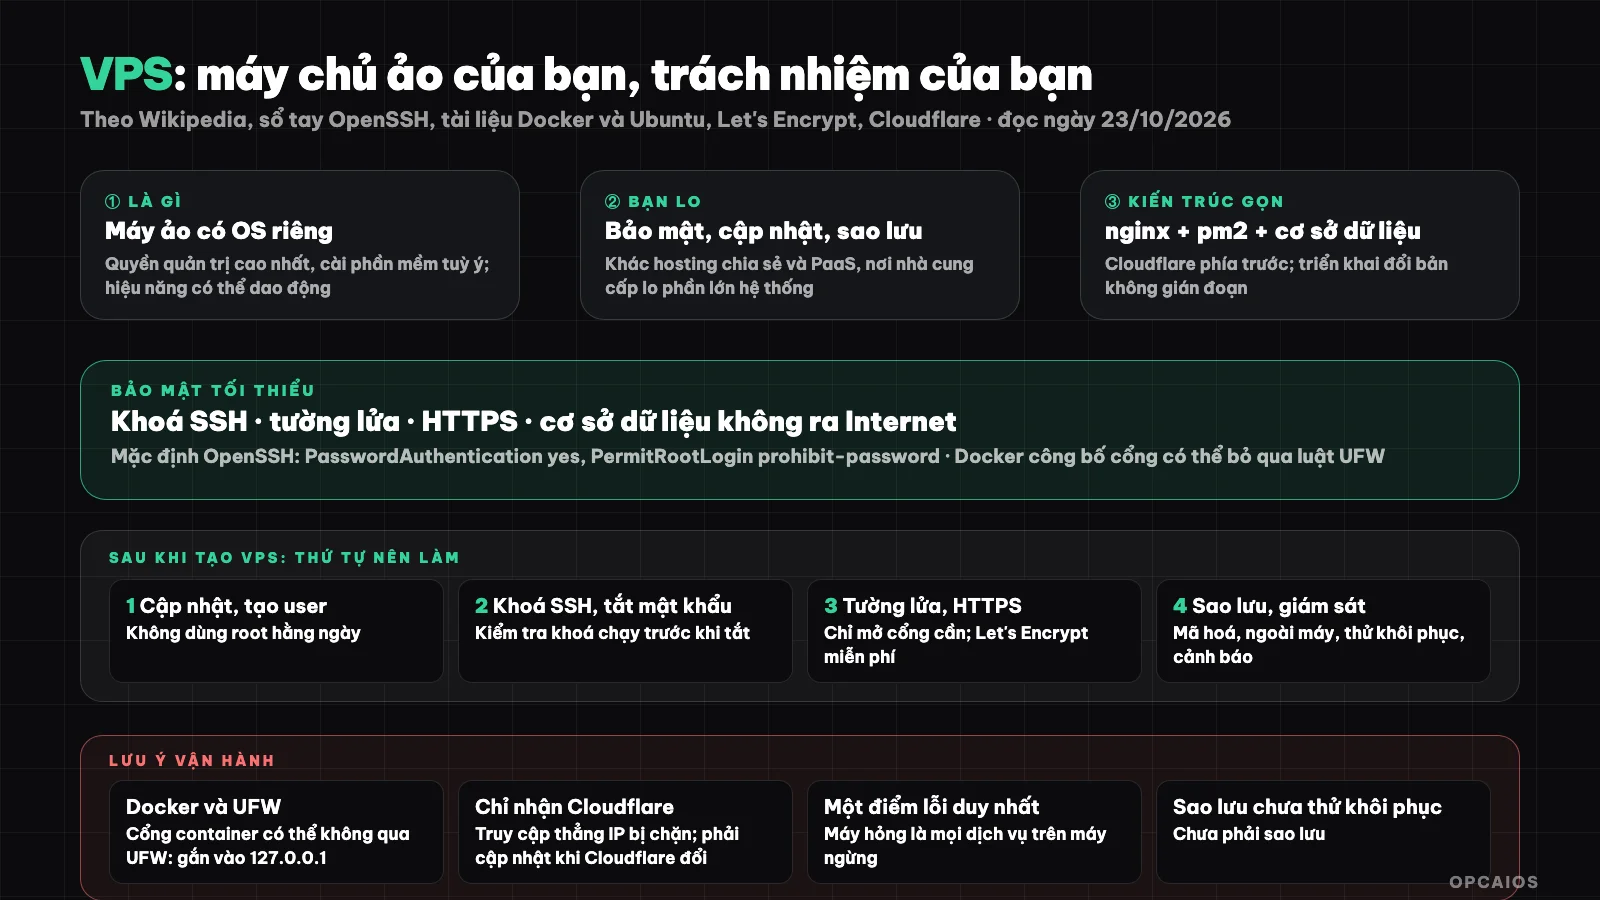
A secure VPS has many layers: only open necessary ports, TLS, database not exposed to the outside network, backups and monitoring. Diagram: OPCAIOS.
What is VPS and how does it work?
VPS is a virtual machine running on a physical server divided into smaller parts by software called a hypervisor. The hypervisor, according to Wikipedia (read 23/10/2026), creates, reclaims and manages resources of "guest" operating systems, and each guest typically only sees the portion of resources allocated to it. Because each VPS has its own operating system, virtual machines are mostly isolated from each other and can restart independently. When you rent a VPS, you get three things. First is a private IP address. Next is SSH access, usually on Linux. Finally is the responsibility to install, secure, update and back up yourself. For example, an Ubuntu VPS using nginx and pm2 can run a Next.js website alongside a database, while the provider only manages the hardware and hypervisor underneath. In exchange, VPS instances share hardware so performance can be lower depending on the load of other virtual machines, according to Wikipedia.
How does VPS differ from shared hosting and PaaS platforms?
It differs in how much you control and how much you have to manage yourself. The table below is a general description to help you choose a direction, not a comparison of specific providers:
| Criteria | Shared hosting | VPS | PaaS (platform as a service) |
|---|---|---|---|
| Control over operating system | Limited | High, with admin privileges | No machine management |
| Who handles OS updates and security | Provider | You | Provider |
| Install software as you want | Limited | Nearly anything that runs on the OS | According to platform model |
| Complexity | Low | Medium to high | Low |
| Suitable for | Simple websites | Multiple services, custom applications, building your own infrastructure | Quick deployment, minimal operations |
What criteria should you use to choose a VPS?
Choosing a VPS is matching your application's real needs with six criteria, not following advertised numbers. For example, a Next.js website with a database needs extra RAM and additional memory for builds, based on OPCAIOS's operational experience. Six criteria to look at (read 23/10/2026) in order:
- CPU, RAM, disk: Extra RAM for heavy applications.
- Server location: closer to users means lower latency; for Vietnamese-language websites, consider nearby regions.
- Backups and snapshots: does the provider have machine-level backups and what's the cost; you should still back up off-machine.
- Bandwidth and IP addresses: limits, IPv4 or IPv6.
- Support and stability: how they handle problems, is there a public status page.
- Payment method and cycle: monthly to make it easy to switch providers.
Prices change quickly so this post doesn't list specific prices; check the current pricing page and backup terms before paying. VPS is cheaper than a dedicated physical server, according to Wikipedia, but performance depends on the load of other virtual machines (according to Wikipedia).
The First Things to Do to Secure a New VPS
Securing a new VPS means closing off every entry point before installing applications, since a newly deployed VPS connected to the Internet is often quickly scanned by automated programs. First, do three foundational things:
- Update the operating system and enable automatic security updates if appropriate.
- Create a separate user and use SSH keys instead of passwords. By default, according to OpenSSH (according to OpenBSD),
PasswordAuthenticationisyes,PubkeyAuthenticationisyes, whilePermitRootLoginisprohibit-passwordandMaxAuthTriesis 6. Disable password login after verifying that SSH keys work, and do not use root for daily tasks. - Enable the firewall and open only necessary ports (SSH, 80, 443). On Ubuntu, UFW is a simple tool: open ports with
ufw allowand check withufw status.
Next are matters about Docker, HTTPS, and databases in the following section (OpenSSH and Ubuntu documentation, read on 23/10/2026). For example, a new Ubuntu VPS should have a separate user and SSH keys before opening any ports besides 22, 80, and 443.
What Should I Pay Attention to with Docker, HTTPS, and Databases?
After that, handle four more points:
- Be careful with Docker and the firewall. UFW and Docker use firewall rules in incompatible ways, according to Docker (according to Docker): when publishing container ports, traffic is redirected before the INPUT and OUTPUT chains that UFW uses, so UFW rules are bypassed. Only publish ports to 127.0.0.1, place the service behind nginx, and control it through the
DOCKER-USERchain. - Use HTTPS with valid certificates. According to Let's Encrypt, this is a free, automatic, and open certificate authority. OPCAIOS uses Certbot with nginx.
- Do not expose the database to the Internet: keep the database listening only on internal addresses; access management tools through an SSH tunnel.
- Keep secrets out of source code: environment variables, tight file permissions; see What is GitHub? on not putting secrets in repositories.
What Are the Benefits of Putting Cloudflare in Front of Your VPS?
Cloudflare acts as a reverse proxy standing between users and your server: users talk to Cloudflare, Cloudflare talks to your VPS. See the overview in What is Cloudflare?. A useful layer of protection is to configure your origin server to only accept connections from Cloudflare's IP ranges, so anyone connecting directly to your VPS's IP address cannot get in. Cloudflare publishes the official list of IPv4 and IPv6 ranges at cloudflare.com/ips (the page notes these as the "official" source of the ranges). One drawback to remember: when Cloudflare updates the list, you must update your configuration accordingly, or real users might be blocked.
How Do I Run a Website on a VPS Cleanly?
Running a website on a VPS cleanly means using a lightweight three-layer model: nginx as the web server and TLS terminator, a process manager like pm2 to keep the application running, and a database on the same machine or another machine. Three things that reduce operational headaches, according to OPCAIOS's experience (documented in 2026):
- Deployment with zero downtime: build the new version in a separate directory while the old version still serves traffic, then switch to the new version. Previously OPCAIOS would build directly on the running version, causing the site to error for 1 to 2 minutes. See the test run steps in What is Vibe coding?.
- Backup correctly: encrypt, store outside the machine (different provider or different region), on a schedule, and tested for restoration, like backups to Google Drive kept for 60 days.
- Monitor and alert: check the website every 5 minutes and notify by phone if it goes down, disk fills up, or backup fails; see how to use a bot in What is a Telegram bot?.
For example, a Next.js website using pm2 behind nginx only needs to swap versions when the build completes, so a faulty build does not break the running website.
OPCAIOS's Experience Running a Website on VPS
I run a website on a VPS along with several other internal services: nginx up front, application processes managed by pm2, a self-hosted Supabase database (see What is Supabase?), and Cloudflare in front. Here are some lessons I've learned, without going into sensitive configuration details.
How are OPCAIOS's security and access?
The first two security lessons (noted in 2026):
- A VPS running multiple services compounds risk. One forgotten open port from one service is a gateway to the entire machine. I have a custom firewall script that opens only necessary ports, blocks container ports through Docker-specific chains, and admin tools are accessed only through SSH tunnels; after one security review, two admin ports were closed.
- The origin server only accepts Cloudflare: direct access via VPS IP is rejected. Operational consequence: health checks must go through the domain name, and Cloudflare's IP list needs to be updated when Cloudflare changes it.
How are OPCAIOS's deployment, database, backups, and monitoring?
Four more operational lessons:
- Deployment using zero-downtime rolling updates: previously I built directly on the running version, which caused 1-2 minutes of site errors; a failed build now doesn't break the website. At the same time, there was once an incident because an environment config change left only one variable missing and the site quietly reverted to old data, so after each config file change I verify all variables are present.
- Database connection limits: once I ran out of connections on the connection pool port, causing a failed build and the website returning 502 errors; since then the application uses transaction-level pooling, and when the database goes down, an alert goes to my phone.
- Encrypted backups to Google Drive, kept for 60 days and already tested restore; the decryption password is stored in two places because if I lose both, the backups are unreadable.
- Monitoring: check the website and database every 5 minutes, alert via Telegram when down and when back up, plus alerts for missing backups or nearly full disk.
Real Risks and Costs of VPS
Cost isn't just rent: it's your time. Main risks include a single point of failure (machine breaks or provider has an outage and everything stops), security responsibility falls on you, and you have to track updates. If you don't want to run your own infrastructure, PaaS or managed hosting might be better. If you let an AI agent run commands on your VPS for you, use a minimum-privilege account, review destructive commands and have backups first; see What is MCP?.
Read more: Guide to setting up n8n on VPS and automating business processes from A-Z for Solopreneurs; Security audit of a one-person website, 6 best website deployment platforms in 2026 for non-technical people.
Frequently Asked Questions
What is a VPS?
It's a virtual machine sold by a hosting provider as a service, running its own operating system and usually giving you the highest administrative rights to install any software you want.
How is VPS different from regular hosting?
VPS gives you control over the operating system and lets you install any software you want, but you have to handle security, updates, and backups yourself; shared hosting is simpler but more restrictive.
What should I do first to secure a new VPS?
Update the operating system, create a separate user, use SSH keys and turn off password login, enable a firewall opening only necessary ports, use HTTPS, don't expose your database to the Internet, and watch out that Docker can bypass UFW rules.
Do I need Cloudflare before a VPS?
Not required, but useful: reverse proxy hides your original server address and can limit the origin server to only accept connections from Cloudflare's IP ranges; you have to update the list when Cloudflare changes it.
How do I back up a VPS correctly?
Proper backup means having an encrypted copy outside the machine, on an automatic schedule and already tested for recovery, based on OPCAIOS's experience (noted in 2026). A backup that hasn't been tested for recovery isn't really a backup. First, encrypt the copy before it leaves the machine. Next, save it somewhere else than your provider or in a different region, because the provider's own snapshots are just an extra layer. Finally, set a schedule and test recovery regularly. For example, OPCAIOS backs up encrypted to Google Drive, keeps 60 days of backups and has tested recovery; the decryption password is stored in two places because losing both would make the backups unreadable. A system checks the website and database every 5 minutes, then alerts via Telegram when they go down, when backups are missing, or when disk space is running low. To learn how to build and operate safe automated infrastructure, see OPCAIOS's AI application training course.
Sources: Wikipedia "Virtual private server"; OpenSSH handbook (sshd_config) at man.openbsd.org; Ubuntu Server documentation on UFW; Docker documentation on packet filtering and firewall (Docker and ufw sections); Cloudflare IP ranges page and Let's Encrypt documentation; read directly on 23/10/2026. Cloudflare Learning blocks automatic access so not used directly. The comparison of hosting types is general description with no detailed sources. Operational experience is OPCAIOS's own; we don't publish specific addresses, ports, or configurations.
Translated from Vietnamese with AI. Read the original.
Want to apply this in your business?
Book a free 30-minute call (Vietnam time, in English or Vietnamese).